Security · IAM

Enterprise security with granular control: 60+ permissions, 3 operator types, and a full audit trail.

Marta Platform implements an IAM (Identity and Access Management) model at enterprise level. Every back-office feature has its own read/write/delete permissions, which you can group into preset or custom roles.

Three operator types — POS, Backend, Platform — each with its own sign-in method. API keys for programmatic access, with control over which operators may use them. Every change is recorded in theaudit trail with who, what and when.

Identity & Access Management

60+ granular permissions, 5 template roles and custom roles for every program

Every back-office feature — customers, promotions, wallets, stores, fraud prevention, analytics — has its own permissions read, write e delete assigned individually. Nothing is implied: if it is not explicitly granted, it is not accessible.

The five template roles cover the most common use cases: POS for terminal operations, Merchant for store management, NetSupervisor for network supervision, ProgramAdmin for full program administration and SystemAdmin for platform management. Each program can add further custom roles.
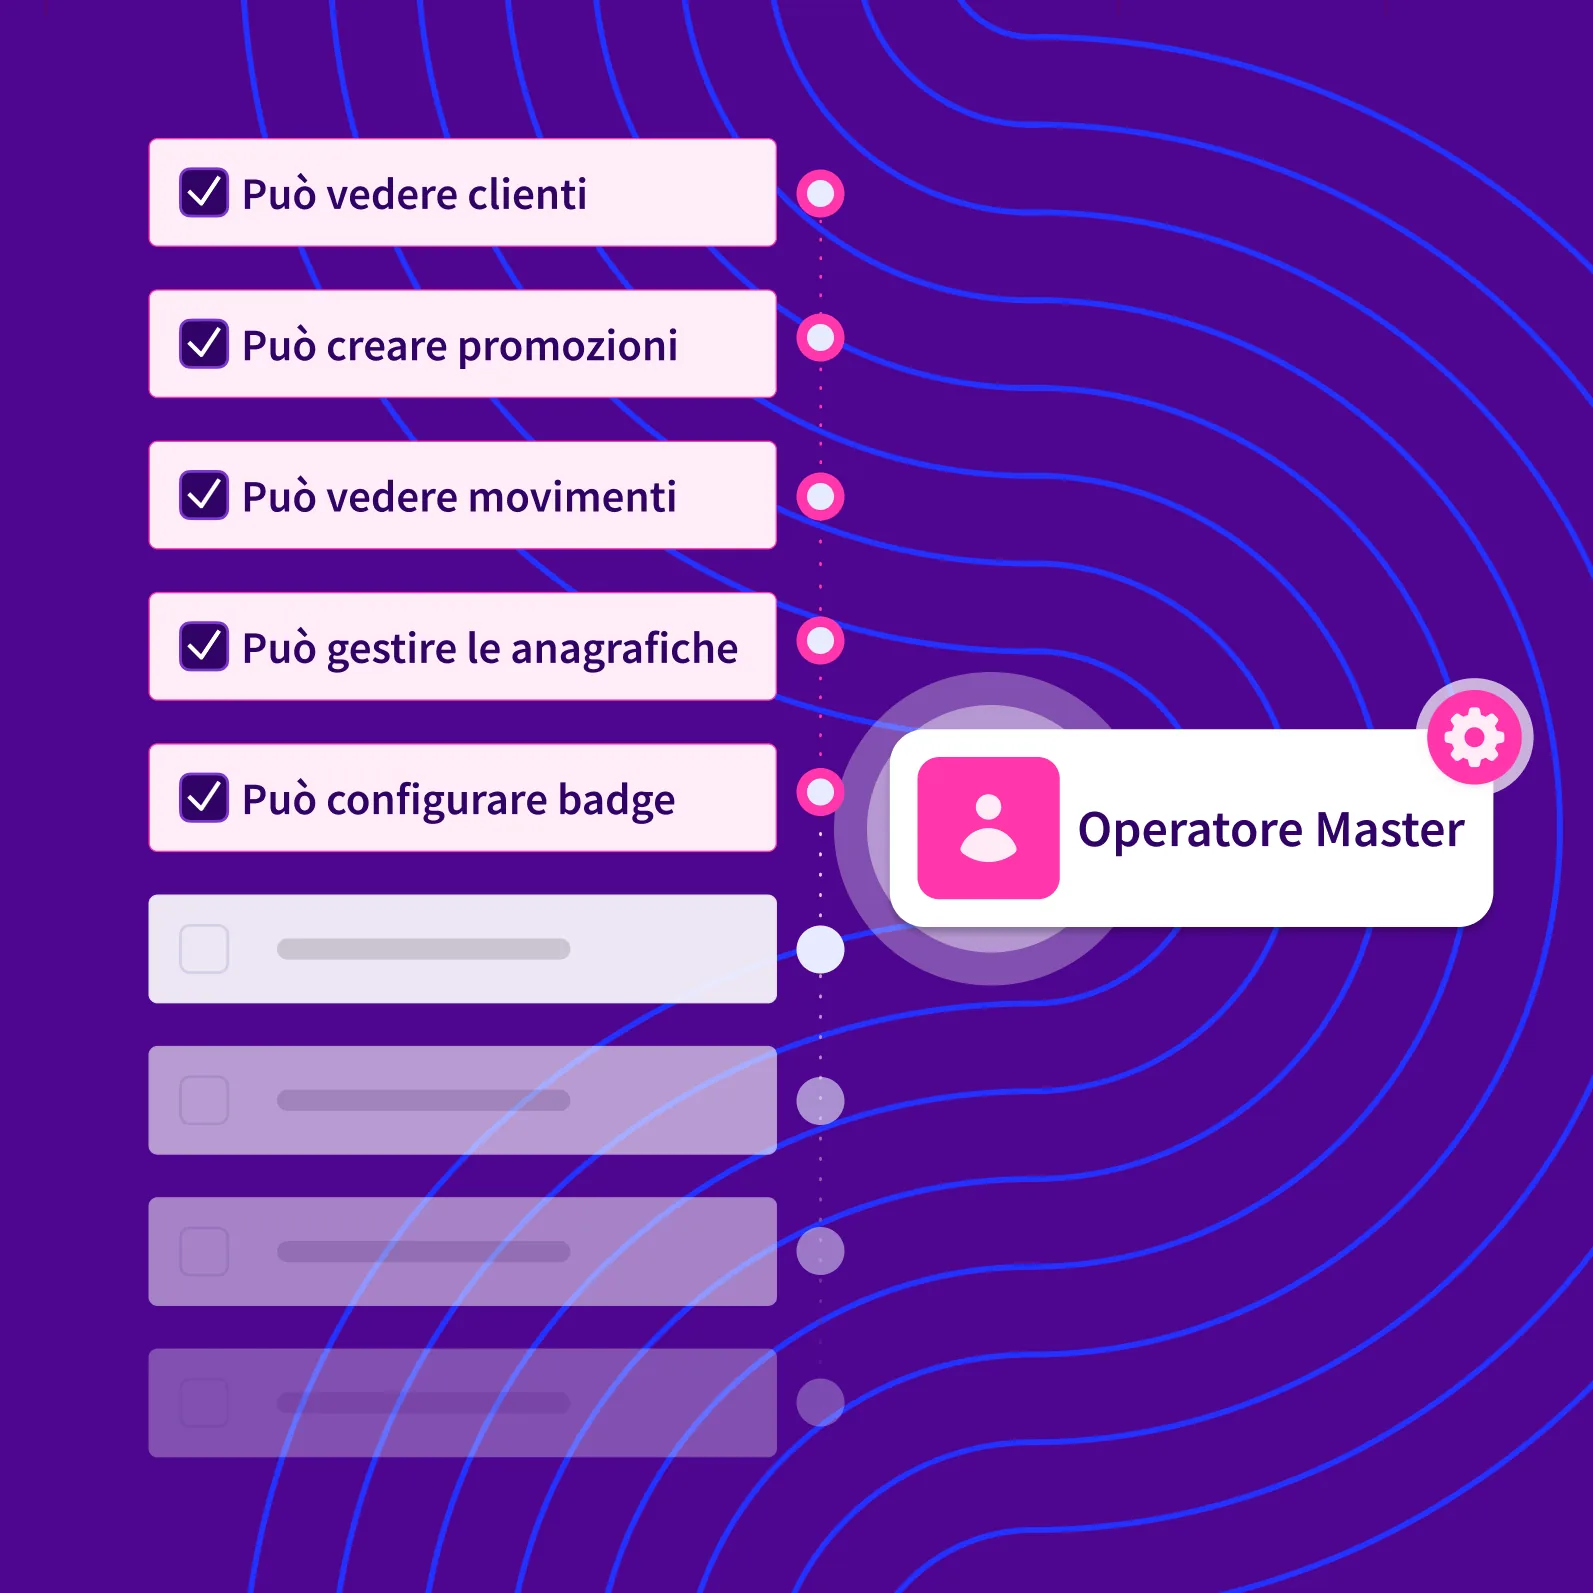
Checklist of operator permissions and the Master Operator role.

Multiple operator types

Three operator types, each with its own authentication: POS, Backend and Platform

Each operator type has a sign-in flow shaped for its own context.

The POS operators sign in with an API Key for a session that stays open at the terminal — the refresh token keeps it active without signing in again. The Backend operators use OAuth/JWT for the web back office, with a scope you can set at program, network or store level. The Platform operators have SYSTEM visibility and can manage more than one program.

A password change is required at first sign-in for every type.

POS operatorAPI Key
For terminal operations: sales, wallets, rewards, Gift Card
Scope: Store · Terminal
Backend operatorOAuth / JWT
For back-office management: customers, promotions, wallets, analytics
Scope: Program · Network · Store
Platform operatorOAuth / JWT
For SYSTEM configuration: program CRUD, system users
Scope: SYSTEM (program_id: null)

Programmatic access

API keys checked per operator: each key enables only the people who should use it

API keys can be set at program or SYSTEM level. No key is generic: it states exactly which operator usernames are allowed to use it. The system checks that the username in the request is on the allow-list for that key.

The authentication flow is: X-API-Key header + username + password → JWT with a refresh token. No key is shared with operators who are not allowed to use it. You can revoke any key immediately without affecting the others.

API Key · Production
Header: X-API-Key
mk_live_3f8a9c2d7e1b4...
Enabled operators:
POS authentication flow
1. POST /auth/token 2. Header: X-API-Key · Body: username + password 3. Response: JWT + refresh_token

Full traceability

Audit trail: every change recorded with who, what and when — no exceptions

Every change made in the back office — creating or editing promotions, updating a customer profile, changing a tier, configuring fraud rules, managing wallets — is written to the audit trail with the operator name, source IP, timestamp and the detail of the operation.

You can review the audit trail from Settings → Audit with filters for operator, period and operation type. It cannot be edited after the fact.

Audit trail · Settings
[email protected] changed the fraud rule "Unusual frequency"
15 Jun 2026, 14:02 · IP: 192.168.1.10
[email protected] updated customer ID #4821 (tier: Silver → Gold)
15 Jun 2026, 13:48 · IP: 10.0.0.22
[email protected] created the promotion "Summer Gold"
15 Jun 2026, 11:20 · IP: 10.0.0.5
[email protected] completed sale MOV #10482 (€42)
15 Jun 2026, 10:55 · Terminal: POS-MI-001

Enterprise security
at every level of the platform

Granular IAM

60+ read/write/delete permissions per feature. 5 template roles plus custom ones. No permission is implied.

PERMISSIONS

3 operator types

POS (API Key), Backend (OAuth/JWT), Platform (OAuth/JWT SYSTEM). Scope you can set per program, network and store.

OPERATORS

API Keys

Keys for a program or SYSTEM, with a list of enabled operators. X-API-Key + OAuth → JWT with a refresh token.

AUTH

Audit trail

Every change recorded: who, what, when, IP. You can filter it, and you cannot edit it afterwards.

TRACEABILITY
All features

Enterprise security with granular control

60+ granular permissions read/write/delete for every back-office section, with no implied permissions.
5 template roles: POS, Merchant, NetSupervisor, ProgramAdmin, SystemAdmin, plus custom roles per program.
3 operator types: POS (API Key), Backend (OAuth/JWT), Platform (OAuth/JWT SYSTEM), with a configurable scope.
API Keys with an allow-list of operators per key, and a username/API Key check on every request.
OAuth/JWT with a refresh token, a configurable expiry and a mandatory password change at first sign-in.
Full audit trail: every change recorded with operator, IP, timestamp and detail — and it cannot be edited.
Support tickets built in: two-way messages between operator and customer, switched on per program.
Card Whitelists: lists of cards allowed on the program, with overlap checks and a starting wallet at registration.
Cloudflare: traffic goes through Cloudflare, with DDoS protection and a WAF. Public forms are protected by Cloudflare Turnstile.

Enterprise security for your loyalty program

Request a demo and see how the IAM model in Marta Platform protects every feature on the platform.